1
Network & Infrastructure Diagram
Topology overview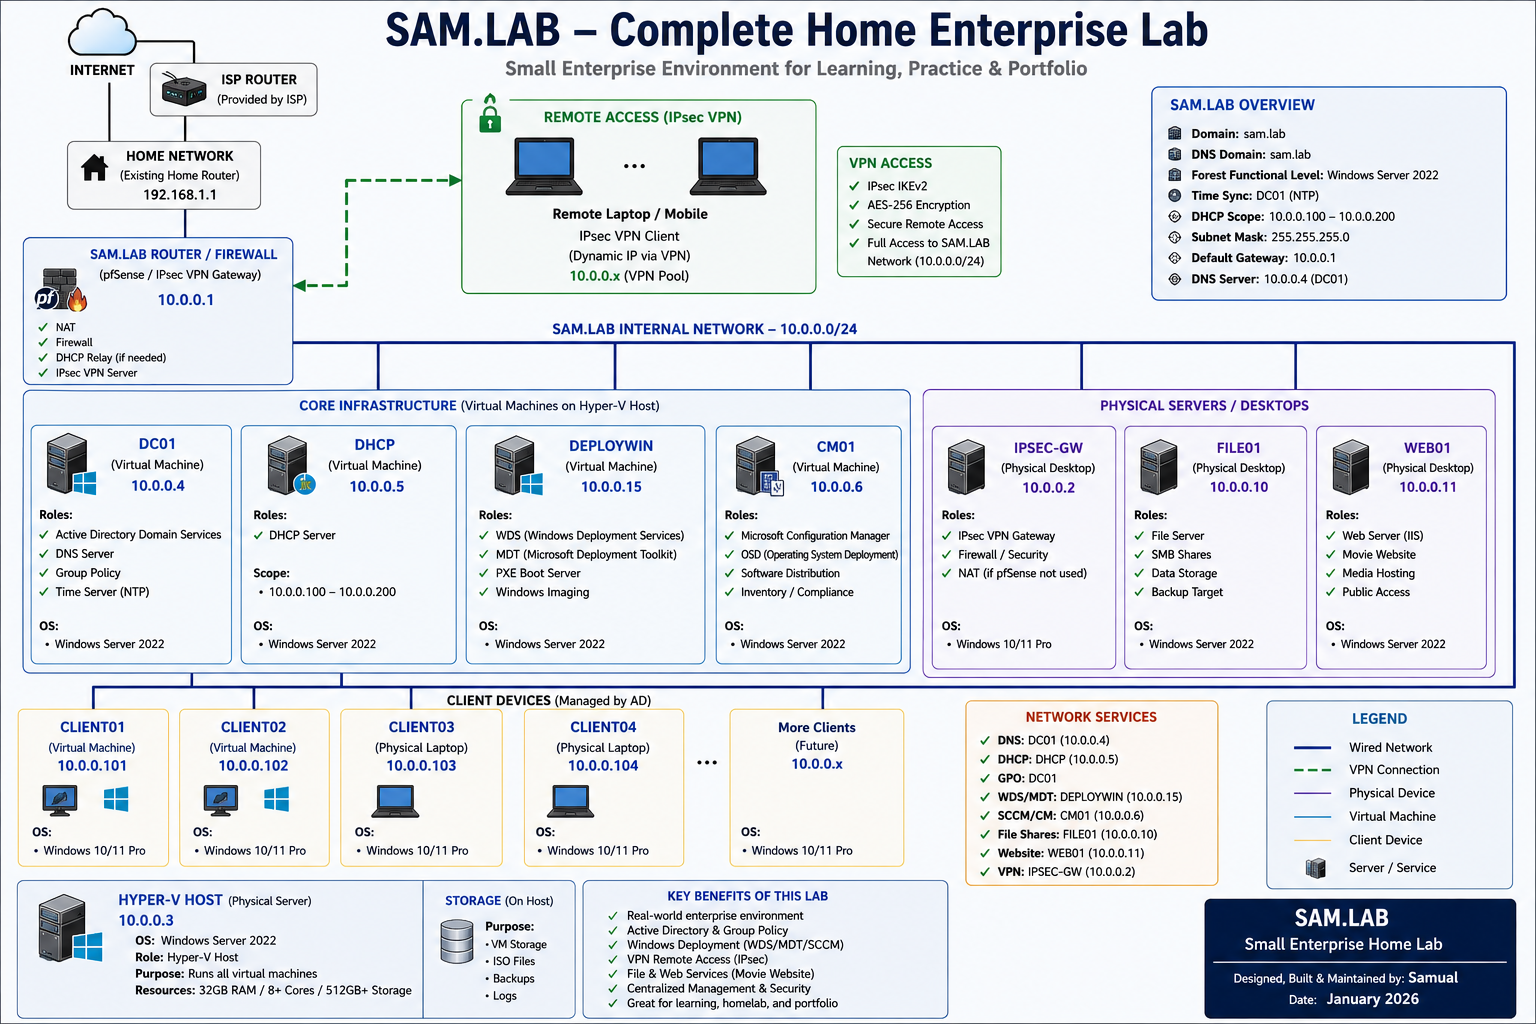
Full topology from the ISP router down through the pfSense/IPsec firewall into the sam.lab internal network — covering core infrastructure VMs (DC01, DHCP, DEPLOYWIN, CM01), physical servers (FILE01, WEB01, IPSEC-GW), the Hyper-V host, and managed client devices.
2
Security & Management Policies
Group Policy & hardening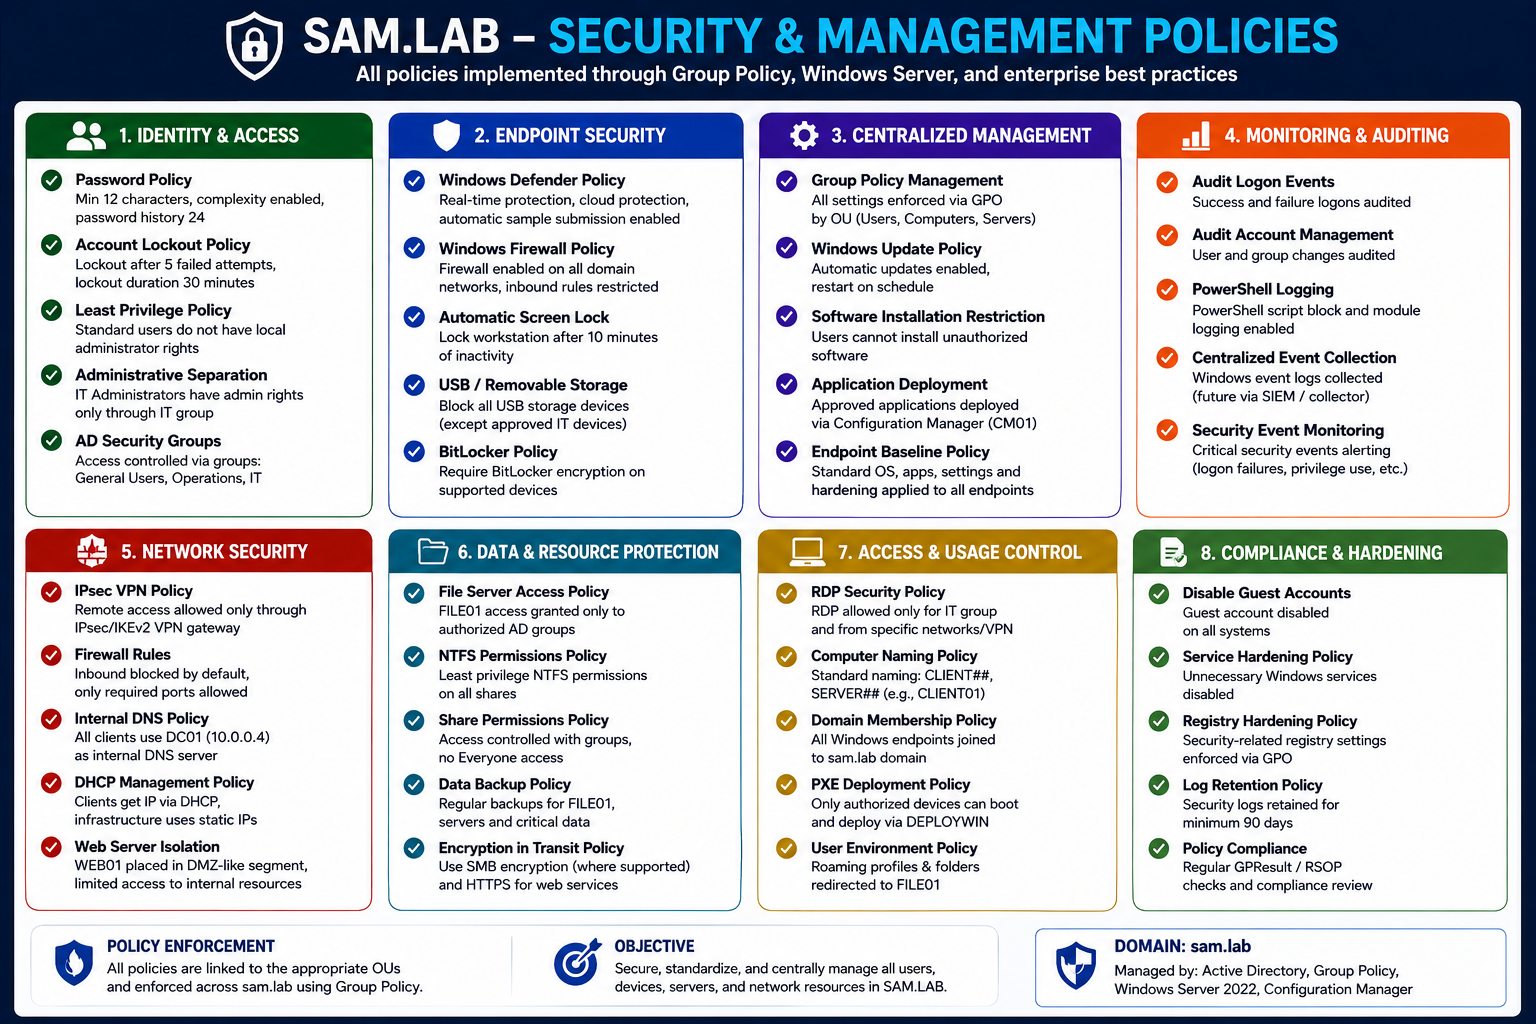
All policies enforced across the domain via Group Policy — spanning identity & access, endpoint security, centralized management, monitoring & auditing, network security, data protection, access control, and compliance hardening.
3
Core Applications Implemented
Enterprise IT · SOC · Network Security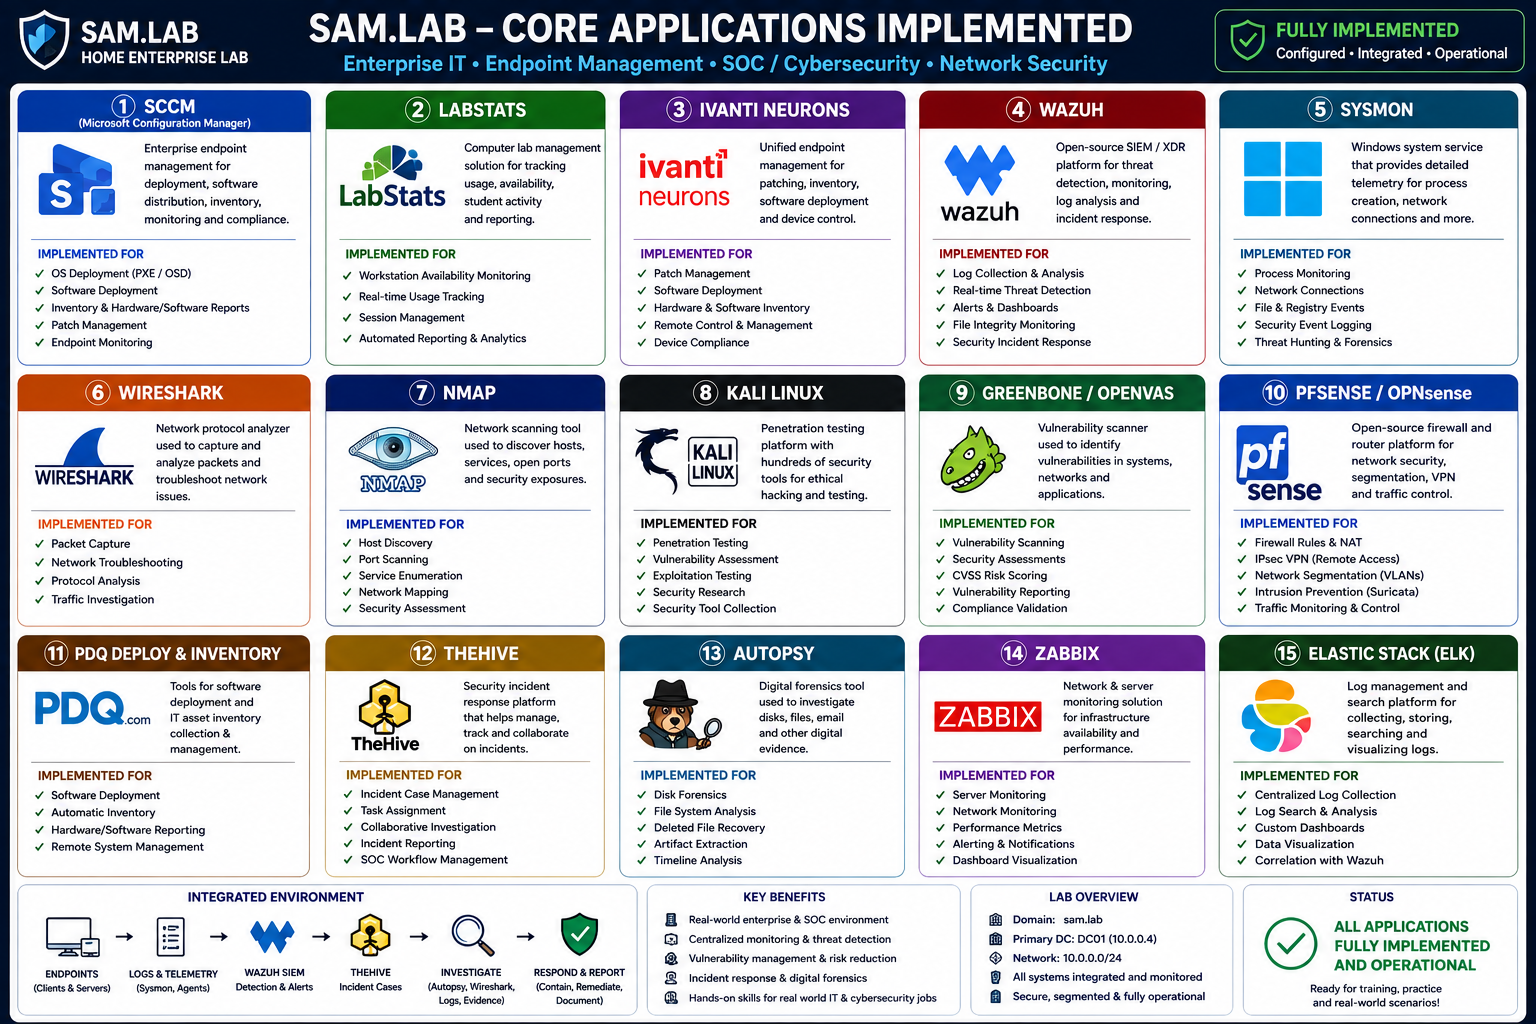
Fifteen tools configured, integrated, and operational — including SCCM, Ivanti Neurons, Wazuh SIEM/XDR, Sysmon, Wireshark, Nmap, Kali Linux, Greenbone/OpenVAS, pfSense, TheHive, Autopsy, Zabbix, and the Elastic Stack.